

[ Dark web intelligence · Attack surface · Identity · AI-powered ]
AI-powered security for dark web threat intel
AlienGate's AI monitors dark web dumps and stealer logs, delivering noise-free, verified exposure data now with an AI assistant to help you act on threats instantly.
[ What we find]
Four kinds of exposure, one place to see them
Every finding arrives with the source it came from and a confidence grade.

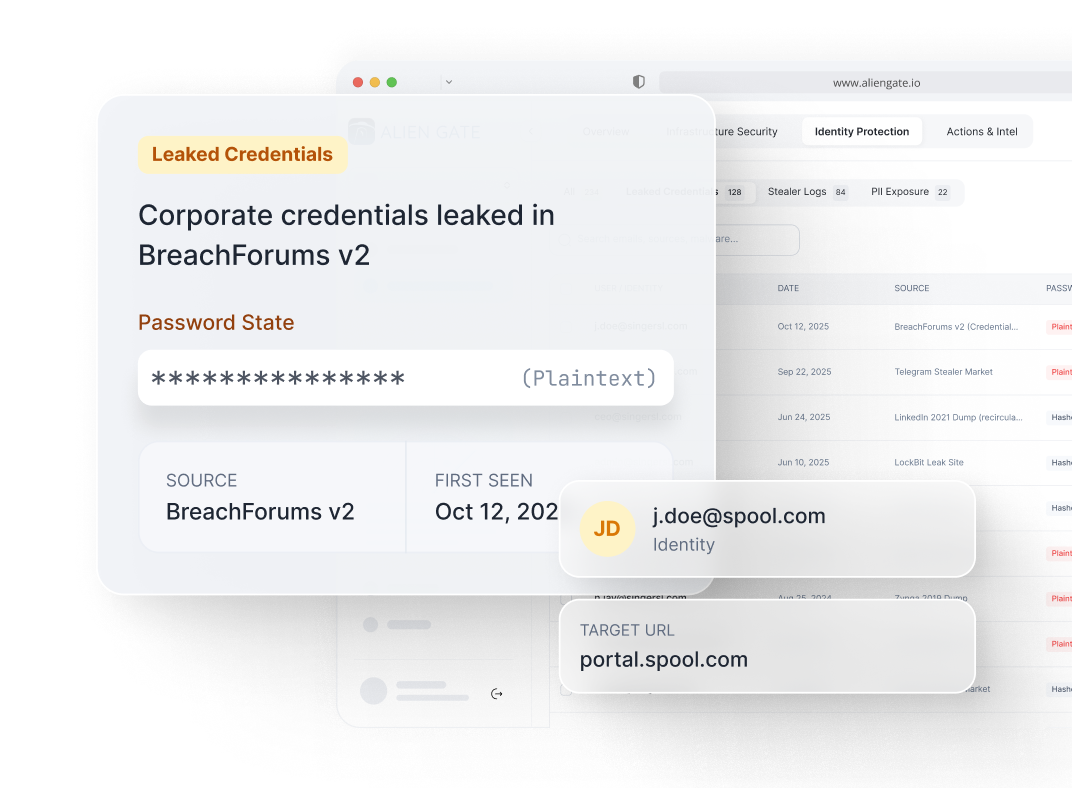
Leaked credentials
Your logins are already for sale. We match combolists, forum dumps and paste mirrors against your domains, then grade every hit before it reaches your queue.

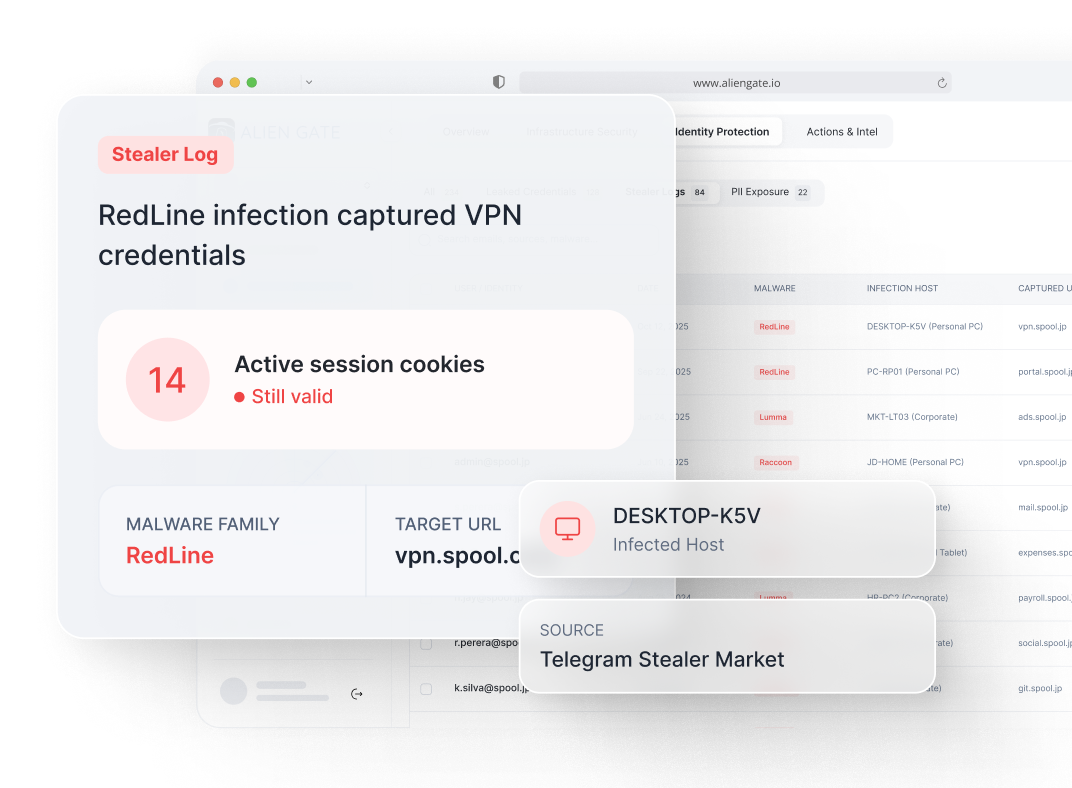
Stealer logs
The exposure that walks past MFA. Infostealer output carries live session cookies, so rotating the password closes nothing. We flag those separately.

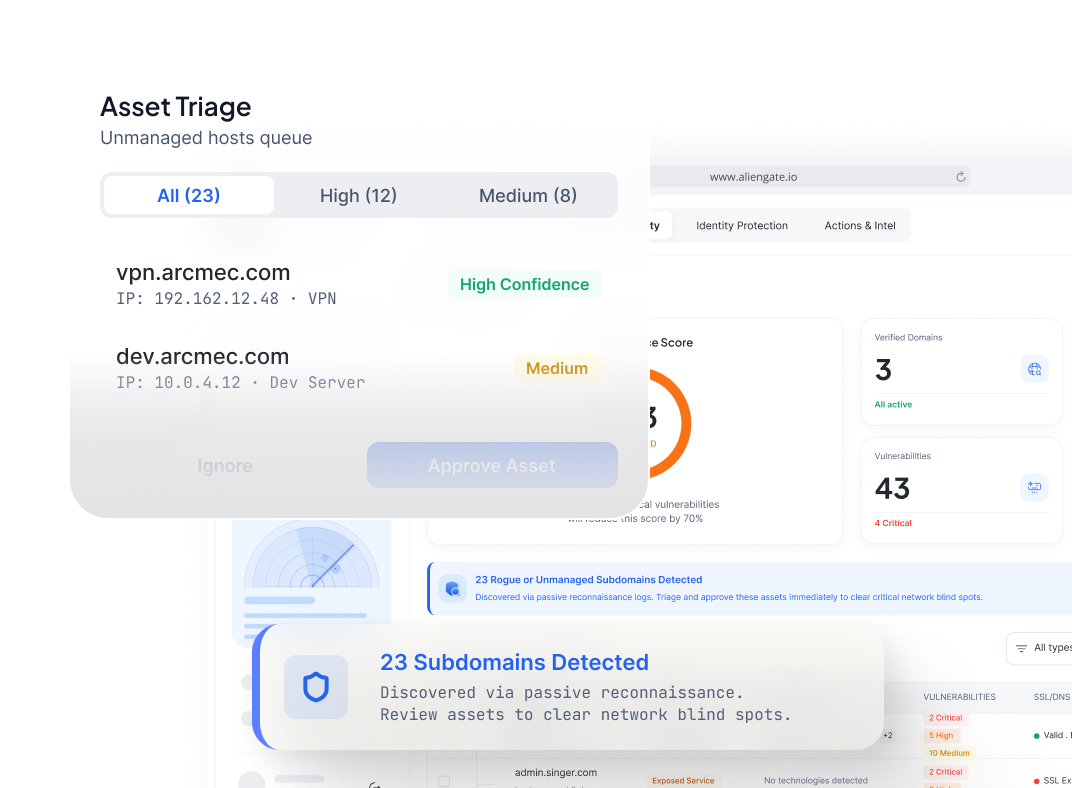
Untracked assets
Shadow IT stops being invisible. Discovery splits everything it finds into managed and untracked, and never merges the two.

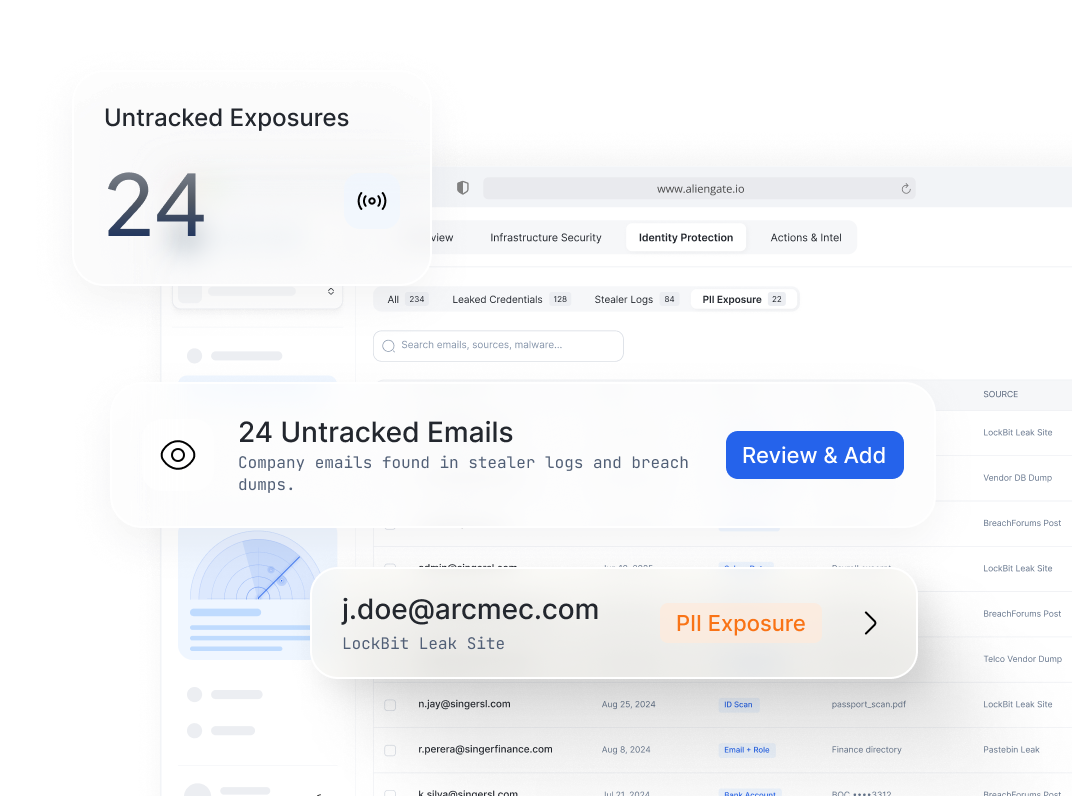
PII exposure
Records circulating beyond your perimeter. Employee and customer data surfacing on ransom leak sites, vendor dumps and private channels.
[ Vulnerability Scanning ]
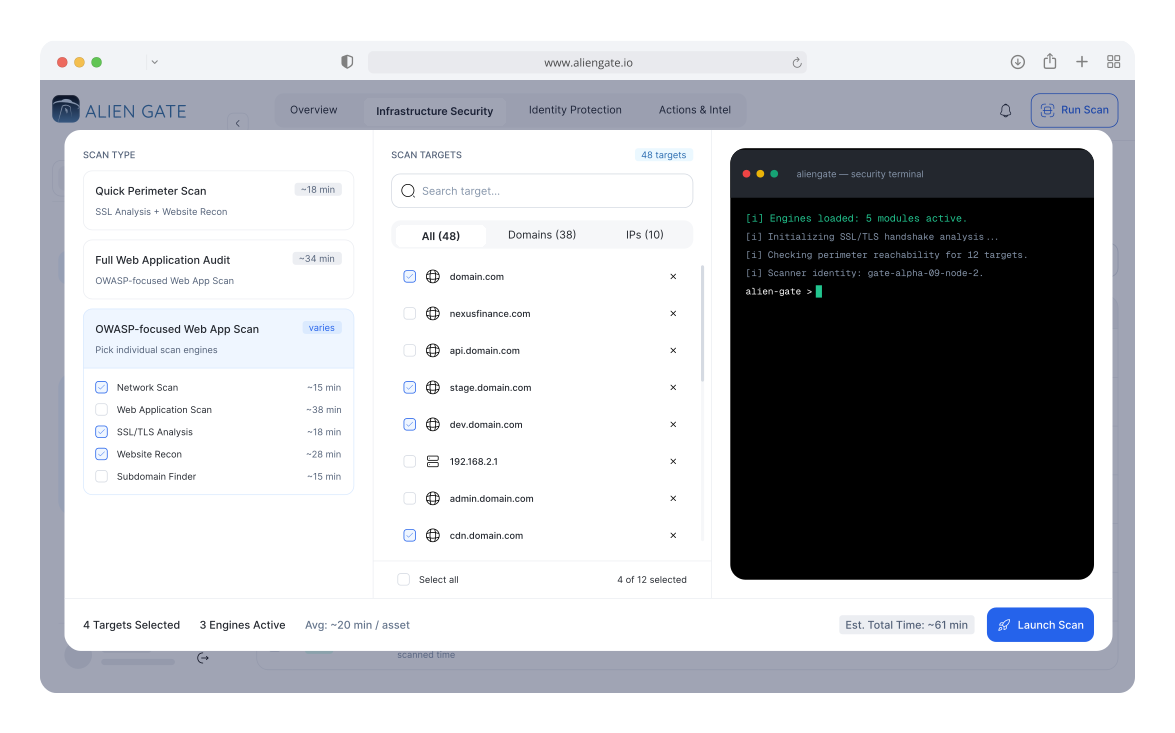
Point it at your perimeter. Get the CVEs before they do.
Five scanning engines run across every domain, subdomain and IP you own. Pick a ready-made profile or compose your own. AlienGate tells you the cost in minutes before a single packet leaves.
[ After the Scan ]
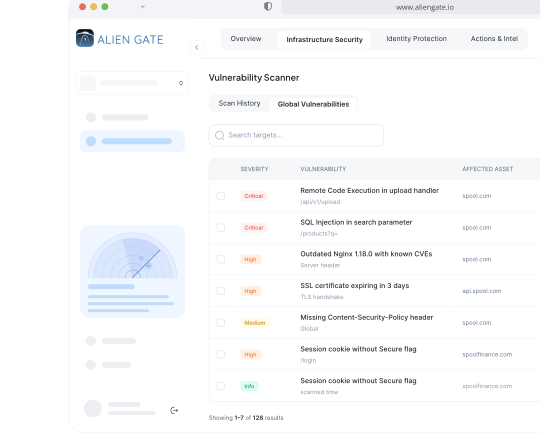
A scan that ends in a list is just more noise.
Every finding arrives severity-ranked, CVE-mapped and tied to the exact asset and endpoint. Then becomes a ticket with an owner and a due date. Nothing waits in a PDF.
[ Who we watch ]
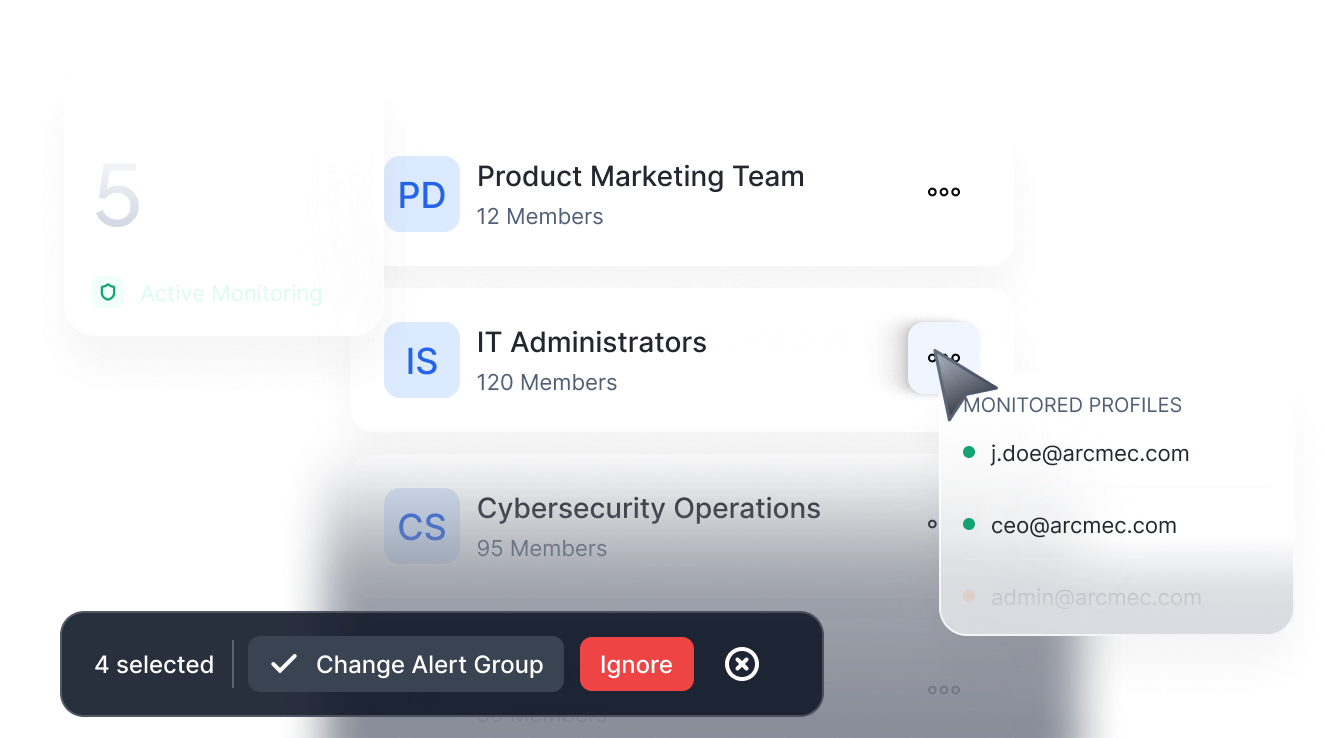
Watch the whole org, not five executives
Three of the four exposure types attach to a person. Identity monitoring is how they find their way to the right inbox.

Alert groups
Your logins are already for sale. We match combolists, forum dumps and paste mirrors against your domains, then grade every hit before it reaches your queue.
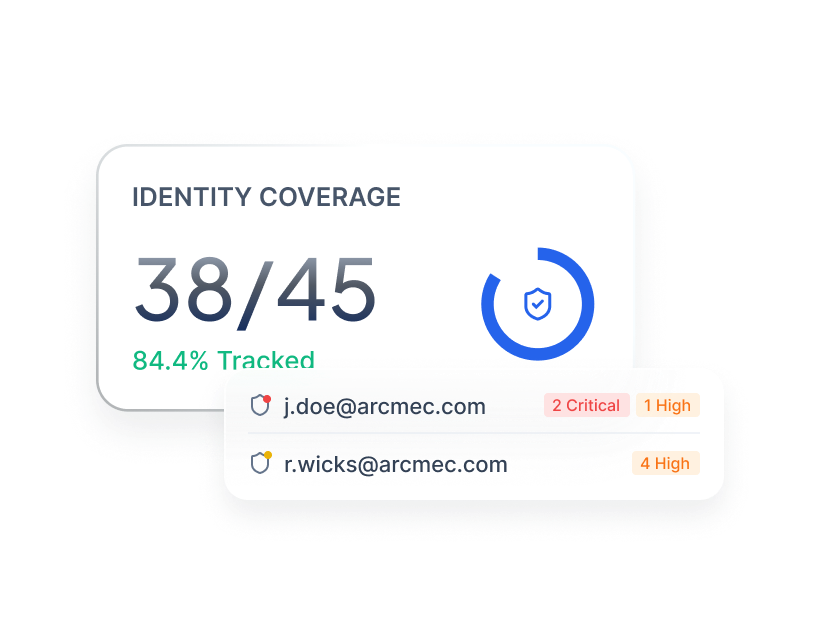

Identity coverage
The exposure that walks past MFA. Coverage is a running ratio, not a checkbox every identity we discover but you haven't tracked shows up as a shortfall.
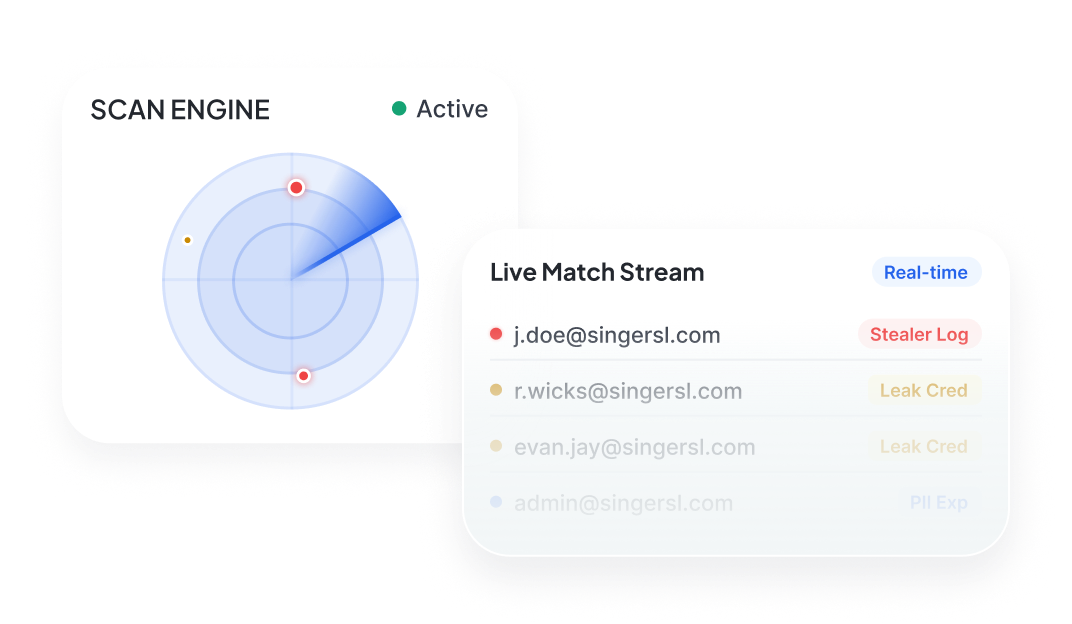

Continuous matching
Your logins are already for sale. We match combolists, forum dumps and paste mirrors against your domains, then grade every hit before it reaches your queue.
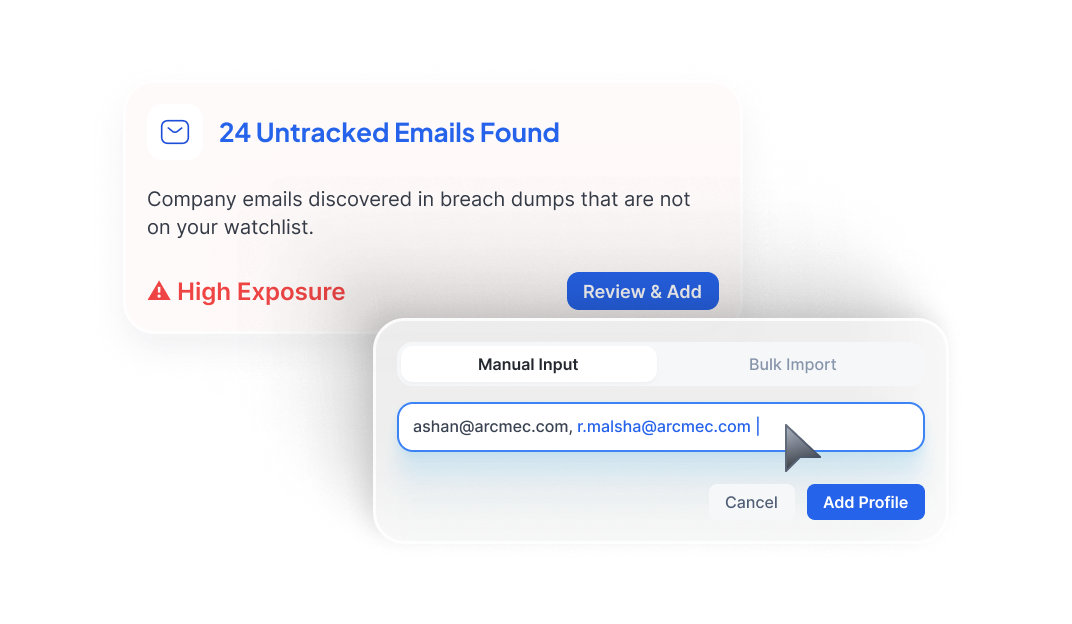

Untracked emails
The exposure that walks past MFA. Coverage is a running ratio, not a checkbox every identity we discover but you haven't tracked shows up as a shortfall.
[ How it works ]
From a leak to an owned ticket
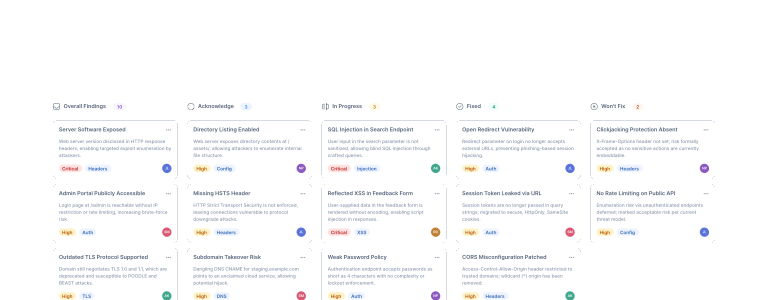
A finding is only useful once someone owns it. This is the path every record takes, and it takes it without you writing a spreadsheet.
STEP 01
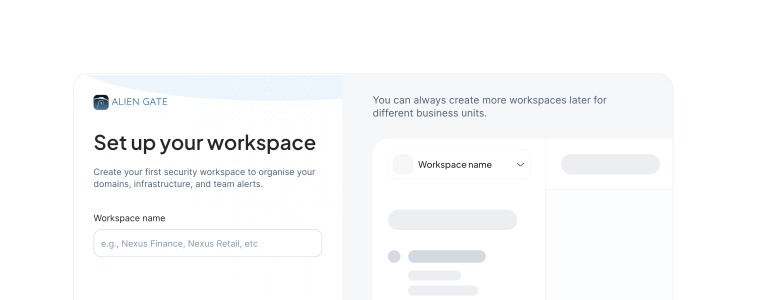
Add a workspace
Sign up with your work email and we provision your first workspace from your domain automatically.
STEP 02
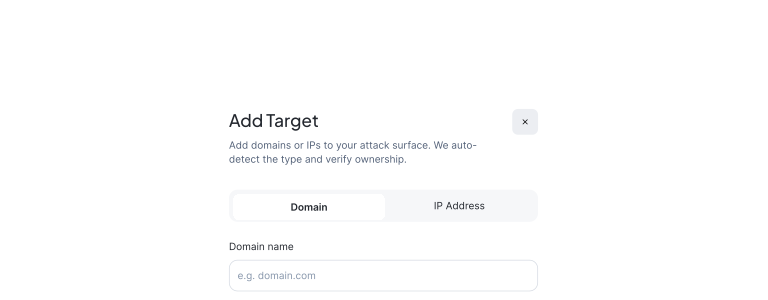
Point us at a target
Add domains, IP ranges and the people worth watching. Discovery runs in the background from the first minute.
STEP 03
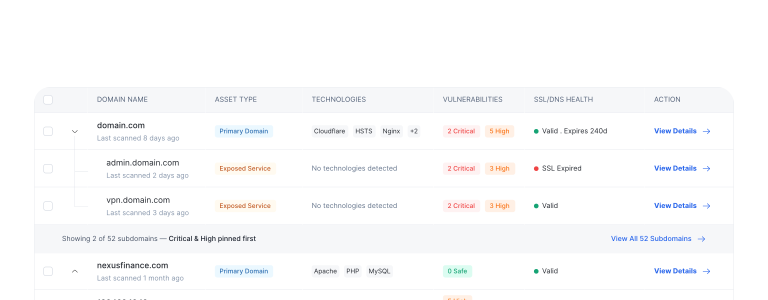
Review what surfaces
Findings arrive graded and sourced. Track the assets that are yours, dismiss the ones that aren't.
STEP 04
Push to your issue tracker
Findings become tickets with owners and due dates, and move across the board until they're closed.
[ How we hold your data ]
We hold the data you'd least like leaked
So our own controls are a product surface, not a compliance afterthought. Full documentation is available under NDA.

Secrets hashed on ingest
Plaintext credentials are hashed the moment they enter the pipeline. Analysts see matches and metadata, never a usable secret.
ENFORCED PLATFORM-WIDE

Workspace isolation
Every object belongs to exactly one workspace. API keys never reach across boundaries — critical for MSSPs running many clients.and metadata, never a usable secret.
ARCHITECTURAL, NOT POLICY

Domain verification required
Identity monitoring only runs on domains you control. You cannot search an address that isn't yours.
ENFORCED AT SIGNUP

Independently assessed
Our own infrastructure is penetration tested by the same standards we apply to customers, under a multi-layer review process.
DOUBLE-CHECK VERIFIED
[ Partners & resellers ]
Delivered through partners, trusted by enterprises
CyberCrew is one of ten group businesses under S-Pool Co., Ltd., listed on the Tokyo Stock Exchange Prime Market.

Tokyo Stock Exchange Prime Market.
30+
Clients Secured
10K+
Total Searches
400k
Monitored Assets
[ Proof ]
Security teams who stopped guessing
MSSPs running dozens of client workspaces, and in-house teams protecting a single one.
FinSecure Corp
AlienGate transformed our threat detection capabilities. The dark web monitoring catches credential leaks within minutes, giving us time to respond before any damage occurs.
TechShield Inc
The platform's ability to map our external attack surface and correlate it with dark web intelligence is unmatched. We've reduced our incident response time by over 70%.
CloudBase Systems
Before AlienGate, we had no visibility into what attackers could see about us. Now we proactively identify and remediate vulnerabilities before they're exploited.
DefenseNet Global
The cyber kill chain integration and automated alerting have been game-changers for our team. AlienGate doesn't just detect threats. It helps us understand and neutralize them.
[ Pricing ]
Choose your security posture plan
Transparent, value-driven tiers scaled specifically for modern tech organizations and CISOs.
Basic
For companies that want to start continuous monitoring
¥50,000
/month (+ tax)
Included Features

Dark web investigation: 1 domain
Email leak check: 500 addresses
Vulnerability assessment: 10 domains
Scan frequency: once a week
Most Popular for CISOs
Premium
For companies looking to strengthen their diagnostics and operational management
¥100,000
/month (+ tax)
Included Features
(Ongoing) Dark web investigation: 3 domains
Email leak check: 2,000 addresses
Vulnerability assessment: 15 targets
Scan frequency: daily
Enterprise
For large-scale operations and individual requirements
¥200,000
/month (+ tax)
Included Features
Dark web investigation: 10 domains
Email leak check: Unlimited
Vulnerability assessment: 20 domains
Custom requirements support
Basic
For companies that want to start continuous monitoring
¥600,000
/year (+ tax)
Included Features
Dark web investigation: 1 domain
Email leak check: 500 addresses
Vulnerability assessment: 10 domains
Scan frequency: once a week
Most Popular for CISOs
Premium
For companies looking to strengthen their diagnostics and operational management
¥1,200,000
/year (+ tax)
Included Features
(Ongoing) Dark web investigation: 3 domains
Email leak check: 2,000 addresses
Vulnerability assessment: 15 targets
Scan frequency: daily
Enterprise
For large-scale operations and individual requirements
¥2,400,000
/year (+ tax)
Included Features
Dark web investigation: 10 domains
Email leak check: Unlimited
Vulnerability assessment: 20 domains
Custom requirements support
[ Faq ]
Frequently asked questions
Everything you need to know about the product and billing.
Our Company
Reach out for product questions, pricing, onboarding, or partnership inquiries.

Headquarters
1-18-13 Sotokanda, Chiyoda-ku, Tokyo 101-0021, Akihabara Daibiru 6F

Founded
April 2025

Shareholder
SPool, Inc. (TSE Prime: 2471)
Find out what's already out there. It takes about forty seconds.
Run a free exposure check on your domain. If it comes back clean, you've lost a minute. If it doesn't, you've found out before someone else did.


