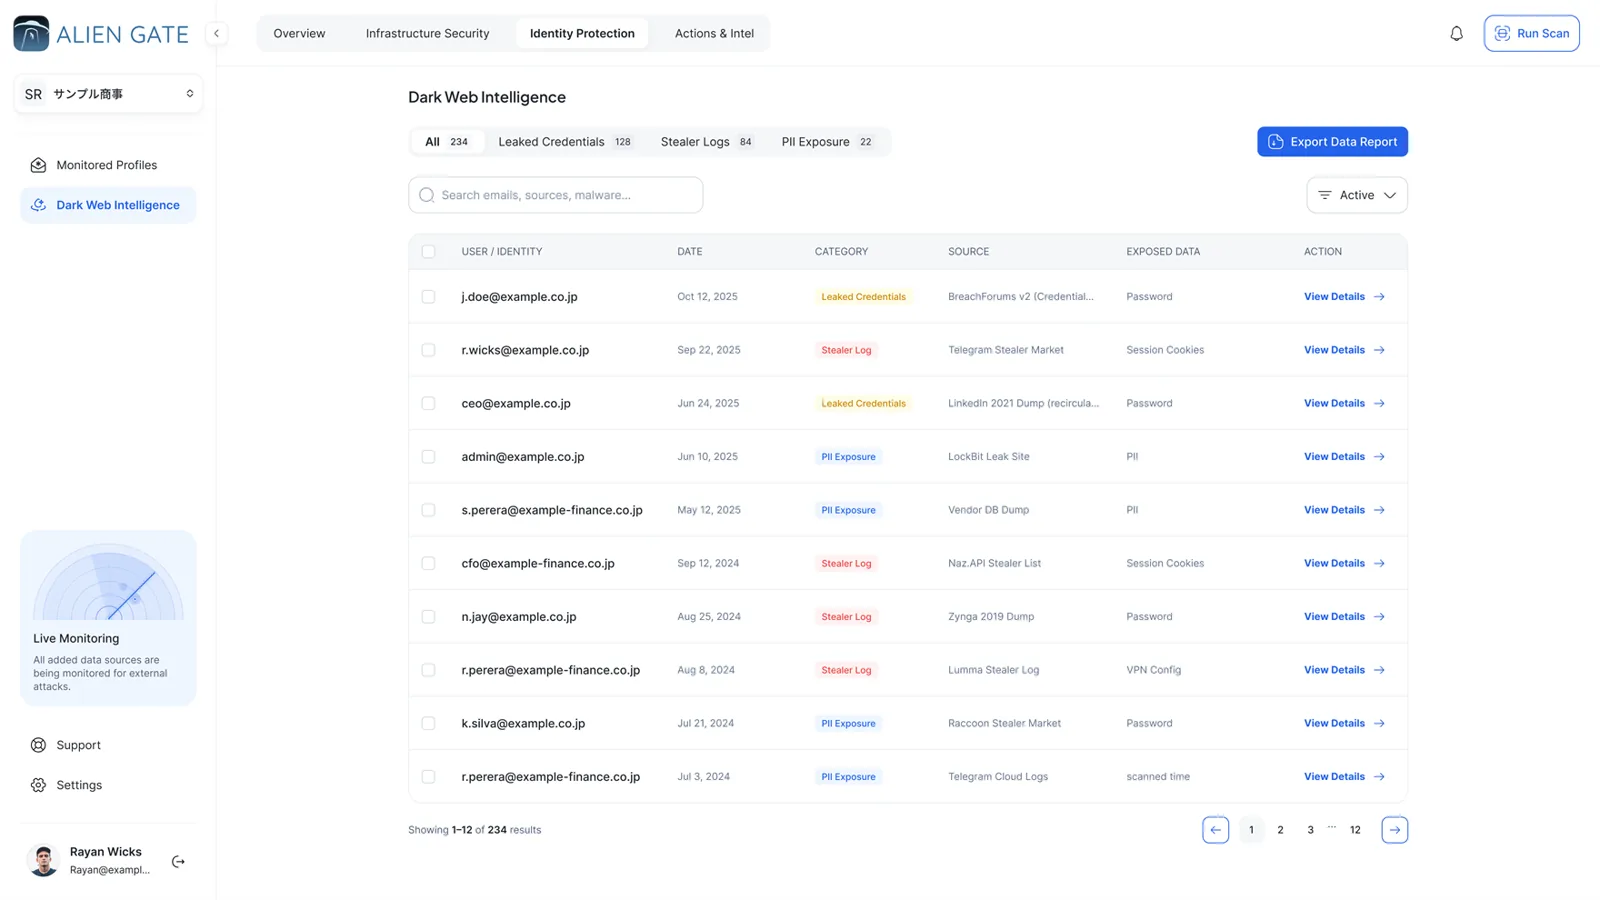


[ Dark Web Intelligence ]
Everything trading with your name on it
Tor and I2P marketplaces, invite-only forums, Telegram channels, ransomware leak sites and infostealer logs, ingested continuously and matched to your domains and people within minutes. Every record arrives with its source, a first-seen time and a confidence grade.
1,800+
Monitored sources
4
Exposure types
Minutes
From ingest to alert
Tor · I2P · Telegram
Where we collect
[ Two services ]
In the console, or through the API
Gain full flexibility. Work the findings in the AlienGate dashboard, or automate the detection of compromised credentials in your own platform through the MISP API.
Try the APICompromised Credentials Monitoring
- Dark web marketplaces
- Combo-lists
- Infostealer logs
50million
Records updated daily
5min
Alert time
Dark Web Monitoring
- Hacking-related Telegram groups and channels
- Dark web forums
- Ransomware leak sites
1,800+
Monitored sources
24/7
Continuous ingest
[ What we find ]
Four kinds of exposure, one place to see them
Every finding arrives with the source it came from and a confidence grade, normalised and deduplicated, so the same dump reposted five times is one record.
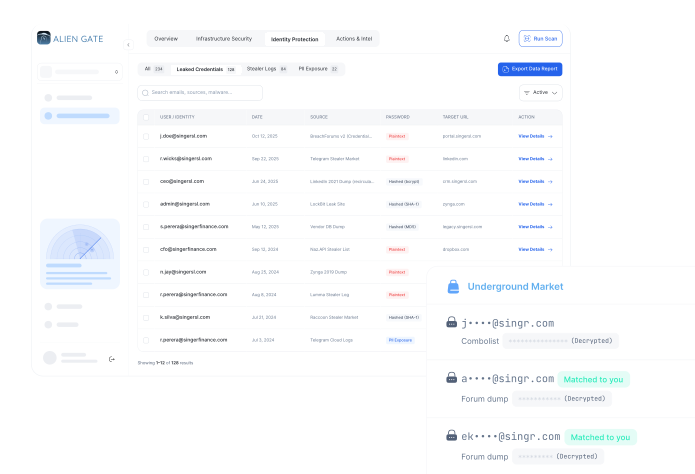

Leaked credentials
Logins already for sale
Combo-lists and forum dumps matched to your domains, normalized and deduplicated.
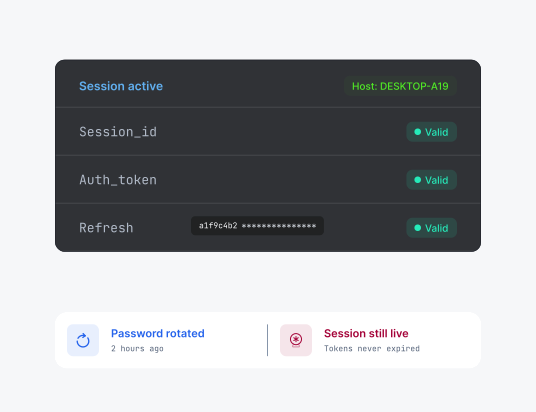

Leaked credentials
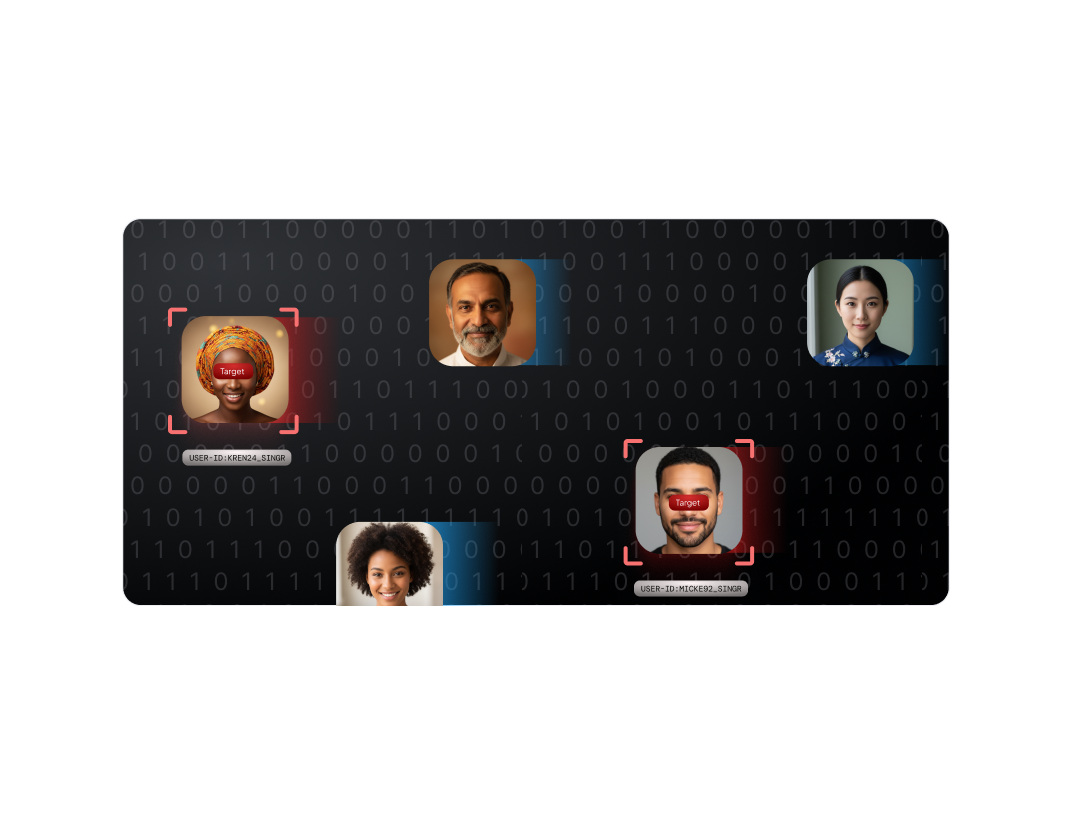
Stealer logs
Live session cookies and tokens. Rotating the password closes nothing.

PII exposure
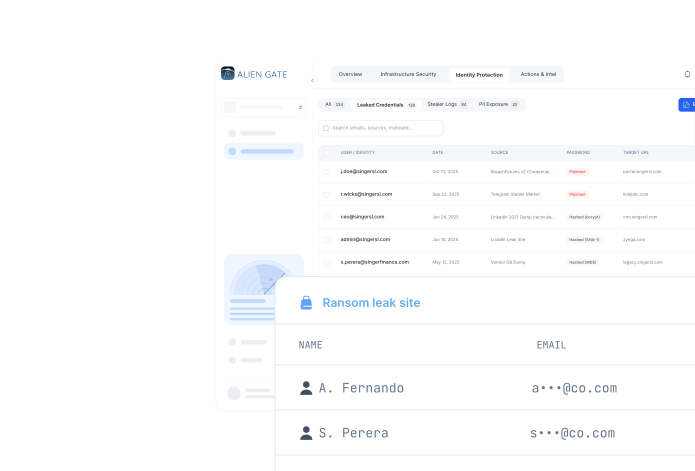
Records in the open
Employee and customer data on ransom leak sites, vendor dumps and channels.

Source coverage
Named, never "the dark web"
Every record carries its origin, a first-seen timestamp and a confidence grade.
[ Coverage ]
Collected where stolen access actually changes hands
Several collection channels combined, so monitoring is broad, current and actionable. The full list of monitored leak sites, markets and channels is on the Database page.
Marketplaces and leak shops
Listings of stolen credentials, access packages and corporate data bundles tied to your domains.
01 · MARKETS

Forums and closed communities
Threads where credential packs are validated, sold and reused for account takeover.
02 · FORUMS

Messaging channels
High-velocity Telegram channels where combo lists and stealer logs are shared before they reach the larger markets.
03 · CHANNELS
Infostealer logs and leak sites
Machine-level credential theft mapped to the affected identity, and ransomware leak sites that name your organisation.
04 · LOGS
[ Signal to action ]
What each source reveals, and what to do about it
The response differs by source. A reused password and a live session cookie are not the same incident, and the alert says which one you have.
Source
What we detect
Recommended action
Combo lists
Email and password pairs reused across breached services
Force a password reset and enforce MFA on the affected users
Stealer logs
Session tokens, saved browser credentials, host metadata
Revoke sessions, rotate secrets and isolate the suspicious host
Marketplace listings
Corporate account access offered for sale
Prioritise the affected business unit and tighten privileged access
Ransomware leak sites
Your organisation, or a supplier, named as a victim with published data
Open an incident, assess the exposed records and notify affected people
Forum mentions
Early chatter about leaked assets and target reconnaissance
Widen the monitoring scope and prepare containment ahead of time
[ Response playbook ]
From detection to hardening, in four steps
A practical workflow teams can run every time. Each step is a state on the Issue Tracker, so the board shows where every exposure sits.

Detect
Leaked data is correlated against your monitored domains, identities and brands as it is ingested.
01 · DETECT

Triage
Each alert is graded by exposure type, the likelihood of credential reuse and the privilege of the account.
02 · TRIAGE

Contain
Revoke risky sessions, rotate credentials and route the alert to the team that owns the affected people.
03 · CONTAIN

Harden
Use the recurring exposure patterns to strengthen authentication and cut repeat incidents.
04 · HARDEN
[ Who it is for ]
One record, three readers
The analyst needs the evidence, IT needs the list of accounts, leadership needs the trend. The same alert serves all three.
01 · SOC
Security operations
Immediate visibility into leaked corporate credentials, alerts prioritised with evidence, and less manual triage of identity incidents.
02 · IDENTITY & IT
Identity and IT teams
Password resets targeted at the people actually affected, adaptive MFA on risky accounts, and a view of repeat exposure over time.
03 · LEADERSHIP
Leadership and compliance
Exposure-to-remediation performance measured over time, and an identity risk posture that can be reported to the board.
[ How it is scoped ]
Scoped to the workspace, never shared between clients
Built for people running more than one entity: MSSPs, holding groups, and anyone whose board asks about subsidiaries.
Workspace, target, asset
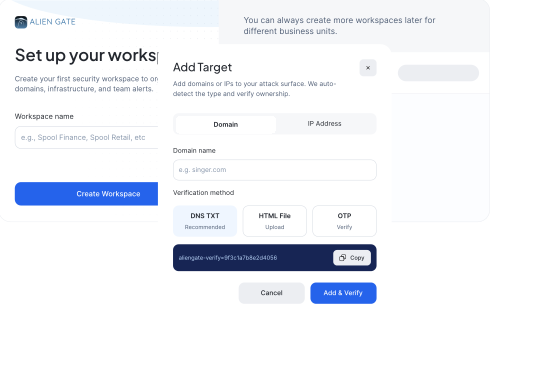
Every object belongs to exactly one workspace. Switch it and the dark web view, the identity view and the scanner re-fetch together. No shared state, no bleed between clients.
Workspace A client, subsidiary or business unit. Provisioned automatically from your email domain on signup.
Target A domain, IP range, or security group of people. Monitoring starts the minute you add one.
Asset inventory Everything discovered under a target, split into managed and untracked.
[ Faq ]
Frequently asked questions
The questions teams ask before they switch on dark web monitoring.
Find out what's already out there. It takes about forty seconds.
Run a free exposure check on your domain. If it comes back clean, you've lost a minute. If it doesn't, you've found out before someone else did.


