Since the 2021 WhatsApp privacy controversy, threat actors have prioritized anonymity and security and have increasingly turned to Telegram. With its strong encryption, capacity for very large groups and lax oversight, Telegram has become a major hub for dark web activity.
It is also worth understanding the leaked data shared on Telegram.
Leaked data is shared there, stealer logs (data stolen by malware) are bought and sold, and cyberattacks are planned.
[Warning] The Telegram channels and groups introduced in this article are extremely dangerous and are used for cybercrime. Accessing or joining them out of curiosity can lead to malware infection or legal trouble, so never do so.
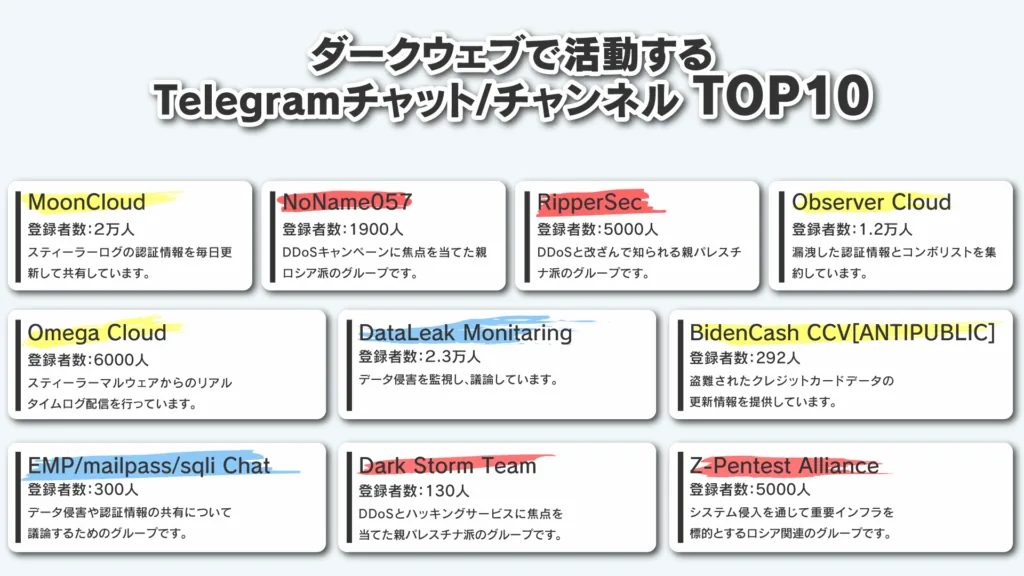
Overview of dark web chat groups and channels on Telegram
Malicious actors are moving activities they once carried out on dark web forums, such as distributing stolen data, spreading malware and planning hacks, onto Telegram. Telegram has introduced AI-based content moderation and begun cracking down on illegal channels, but many channels continue to operate underground.
The evolution of Telegram-based dark web activity
In September 2024, Telegram introduced AI-driven content monitoring. As a result, some cybercriminals moved to Signal, Discord and decentralized messaging platforms. Even so, Telegram remains a central venue for major illegal activity.
CyberCrew's dark web monitoring tools scan Telegram, forums and marketplaces to identify leaked information, exposed corporate data and emerging cyber threats, enabling a rapid response.
How do threat actors abuse Telegram?
Telegram's design enables cybercrime such as the following:
- Sharing and selling stolen data: credentials, credit card information, corporate databases and more
- Providing hacking tools, malware and ransomware
- Planning and carrying out DDoS attacks (targeting governments and companies)
- Sharing vulnerabilities and identifying targets
- Confidential transactions in invitation-only private groups
- Automated credential theft and malware distribution via Telegram bots
- Hacking-for-hire services (website defacement, data intrusion and more)
These activities show that Telegram functions as part of the dark web, not merely as a messaging app. Real-time monitoring is the key to preventing data leaks and unauthorized access.
By tracking activity on underground networks, CyberCrew helps security teams respond quickly.
[Quick explainer: the main types of threat actors on Telegram]
Groups active on Telegram can be broadly classified by their purpose as follows.
- Hacktivists: Groups that carry out DDoS attacks, website defacement and similar actions to advance political or social causes. (Examples: NoName057(16), RipperSec)
- Data brokers / markets: Groups that buy, sell and share stolen credentials (stealer logs), credit card information and the like. (Examples: Moon Cloud, BidenCash)
- Ransomware-related: Channels that leak information stolen in ransomware attacks or share information about attacks. (Example: Data Leak Monitoring)
- Cybercrime communities: Groups engaged in broader criminal activity, such as malware development, discussion of hacking techniques and planning joint attacks. (Example: EMP/mailpass/sqli Chat)
Top 10 notable dark web channels and groups on Telegram
1. Moon Cloud
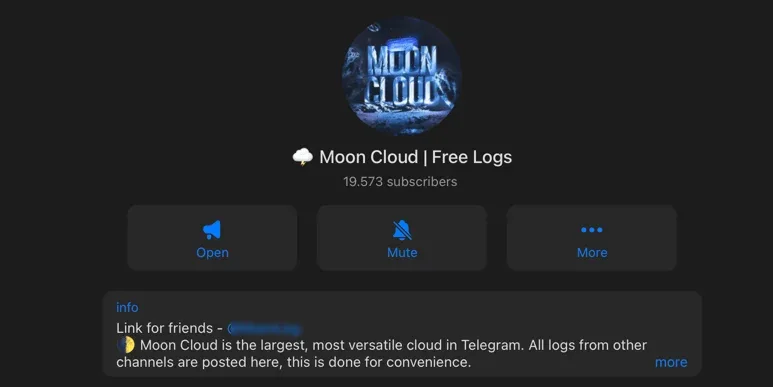
Moon Cloud Telegram channel
Moon Cloud distributes credentials stolen through stealer logs and has 20,000 members. It shares URLs, email addresses, passwords, IP addresses and more, sometimes posting 2,000 new logs a day. Both free and paid services are available.
2. NoName057(16)
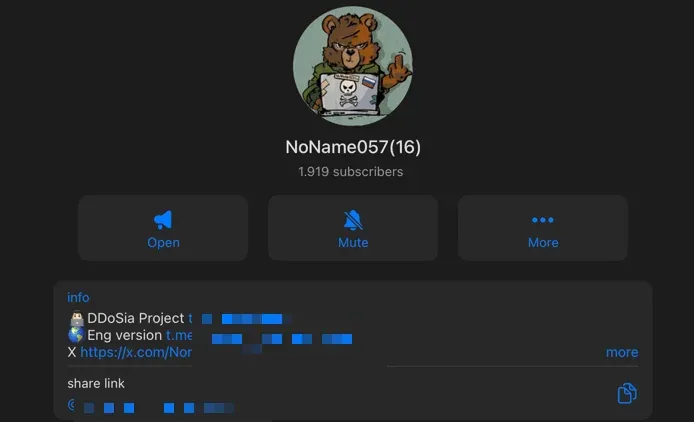
NoName057(16) Telegram channel
A pro-Russian hacktivist group that emerged in March 2022 and has led DDoS attacks against Ukraine and NATO member states. Although Telegram suspended it for a time, it quickly reappeared and has continued its activity.
3. RipperSec
RipperSec DDoS channel
A pro-Palestinian hacktivist group from Malaysia. Since June 2023 it has gained more than 5,000 subscribers and has released DDoS tools such as "MegaMedusa."
4. Observer Cloud
Observer Cloud Telegram channel
Operating since April 2022, with more than 12,000 participants. It collects and shares logs and combo lists, and while it claims an educational purpose, illegal data is in fact exchanged there.
5. Omega Cloud
Omega Cloud Telegram channel
With more than 6,200 subscribers, it distributes logs in real time. Through live traffic and private cloud features, it provides up to 120,000 logs a month.
6. Data Leak Monitoring
Data Leak Monitoring Telegram channel
A channel that shares leaks from ransomware groups and posts from cybercrime forums, with more than 20,000 followers.
7. BidenCash CVV [ANTIPUBLIC]
BidenCash CVV Telegram channel
A market-style channel that publishes stolen credit card information in real time. It illustrates just how quickly stolen card data spreads.
8. EMP/mailpass/sqli Chat
EMP/mailpass/sqli Chat group
A Russian-language cybercrime group active since 2019 that has expanded worldwide. Discussion centers on selling leaked information, SQL injection, malware and similar topics.
9. Dark Storm Team
Dark Storm Team Telegram channel
A pro-Palestinian hacktivist group that has led DDoS attacks against countries around the world. It also offers hacking-for-hire services paid in cryptocurrency.
10. Z‑Pentest Alliance
Z‑Pentest Alliance Telegram channel
A Russian group that began operating in October 2024, carrying out sophisticated intrusions targeting OT systems in sectors such as oil, gas and water treatment.
https://cyber.spool.co.jp/major-cyber-attacks-manufacturing-industry-in-2025/
Stay secure with CyberCrew
Cybercrime that exploits Telegram's anonymity keeps expanding. CyberCrew's monitoring and intelligence solutions respond to these threats in real time and can stop unauthorized access attempts before they escalate into full-scale breaches.
Glossary
| Term | Explanation |
|---|---|
| Stealer logs | Log files compiling information (IDs, passwords, cookies, credit card details and more) stolen from PCs infected with malware (infostealers). |
| Hacktivist | A blend of "hacking" and "activist." An individual or group that carries out cyberattacks to achieve political or social goals. |
| DDoS attack | An attack that floods a specific server with traffic from many computers to force the service offline. |
| OT systems | Short for Operational Technology. Technical systems used to control and monitor factory production lines and critical infrastructure (power, gas, water and so on). |
Consider entrusting the monitoring of closed communities to a specialist provider.